A security group is a virtual firewall that features stateful data packet filtering. It is used to configure the network access control of CVM, CLB, TencentDB, and other instances while controlling their outbound and inbound traffic. It is an important means of network security isolation. You can learn more about security groups in the following video.
You can configure security group rules to allow or reject inbound and outbound traffic of instances within the security group.
Features
A security group is a logical group. You can add CVM, ENI, TencentDB, and other instances in the same region with the same network security isolation requirements to the same security group.
If a security group has no rules, it will reject all traffic by default, and you need to add rules to it to allow traffic.
Security groups are stateful. Inbound traffic you have allowed is automatically allowed to go out and vice versa.
You can modify security group rules at any time, and new rules will take effect immediately.
Usage Limits
For more information on the restrictions and quotas of security groups, please see Use Limits.
Security Group Rules
Components
A security group rule consists of:
Source or Destination: traffic origin (inbound rules) or target (outbound rules). It can be a single IP address, an IP address range, or a security group. For more information, see Security Group Rules.
Protocol:port: Protocol types such as TCP and UDP.
Policy: Allow or reject.
Rule priorities
The rules in a security group are prioritized from top to bottom. The rule at the top of the list has the highest priority and will take effect first, while the rule at the bottom has the lowest priority and will take effect last.
If there is a rule conflict, the rule with the higher priority will prevail by default.
When traffic goes in or out of an instance bound to a security group, the security group rules will be matched sequentially from top to bottom. If a rule is matched successfully and takes effect, the subsequent rules will not be matched.
Multiple Security Groups
An instance can be bound to one or multiple security groups. When it is bound to multiple security groups, the security groups are executed from top to bottom. You can adjust their priorities at any time.
Security group templates
Tencent Cloud provides the following two security group templates:
Template of opening all ports: All inbound and outbound traffic will be allowed to pass.
Template of opening major ports: Port TCP 22 (for Linux SSH login), ports 80 and 443 (for web service), port 3389 (for Windows remote login), and protocol ICMP (for Ping commands) will be open to the public network. In addition, access from the private network (VPC IP ranges) will be allowed.
If you need to protect the application layer (HTTP/HTTPS), you can purchase Tencent Cloud Web Application Firewall (WAF), which provides web security at the application layer to defend against web vulnerabilities, malicious crawlers, and CC attacks, protecting your websites and web applications.
Directions
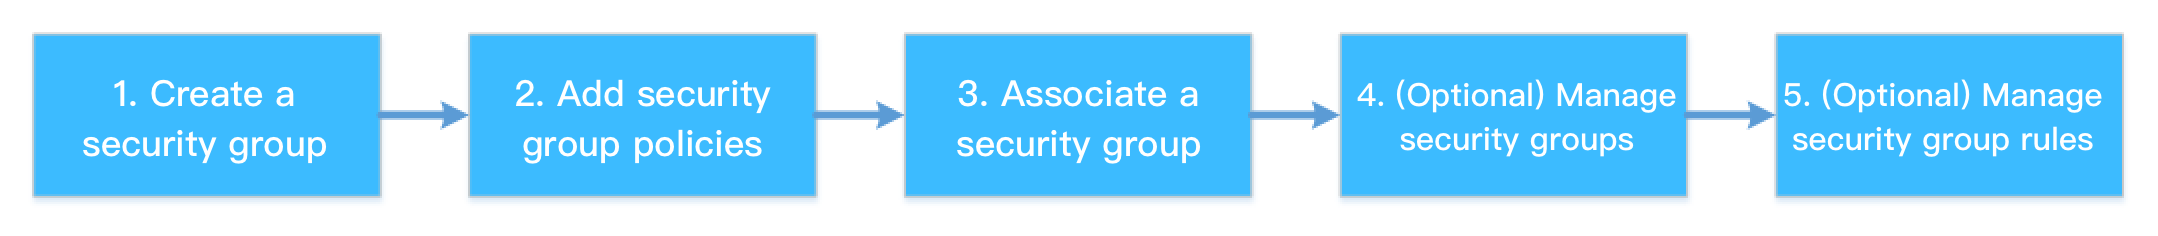
The following figure shows how to use a security group:
Security Group Best Practices
Creating a security group
We recommend you specify a security group when purchasing a CVM instance via the API; otherwise, the default security group will be used. It adopts the default security rule (that is, allowing all IPv4 addresses), which can be modified as needed after the security group is created.
If you need to change the instance protection policy, we recommend you modify the existing rules instead of creating a security group.
Managing rules
Export and back up the security group rules before you modify them, so you can import and restore them if an error occurs.
You can add instances with the same protection requirements to the same security group, instead of configuring a separate security group for each instance.
We recommend you not bind one instance to too many security groups, which may cause rule conflicts and result in network disconnection.
Security Group and Cloud Firewall
Tencent Cloud Firewall (CFW) is a native Tencent Cloud SaaS firewall that integrates different capabilities, including vulnerability scanning, IPS intrusion blocking, internet-wide threat intelligence, and advanced threat source analysis, making it the traffic security and policy management center in the cloud environment. It also serves as the first security portal for cloud business.
In practical use cases, security groups are typically deployed at the boundaries of cloud products such as CVMs to implement access control between security groups. Tencent Cloud Firewall, on the other hand, is deployed at the boundaries between VPCs or the internet to implement access control between VPCs or from Tencent Cloud to the internet.
In scenarios where security groups cannot meet the requirements, you can use Tencent Cloud Firewall to implement access control:
1. You need to understand the exposure and vulnerabilities of CVM assets on the internet and strengthen protection against network vulnerabilities through the IPS intrusion prevention and virtual patching features.
2. When you need to control the proactive access to the Internet by domain name and enhance the business security.
3. You need to implement access control by region, for example, blocking all IPs outside the Chinese mainland quickly.