Risk
Unduh
Mode fokus
Ukuran font
The database risk monitoring module focuses on behaviors that have not triggered risks but pose long-term potential security risks. It covers core scenarios such as permission compliance rectification, attack surface hardening, and account security optimization, reducing the probability of security incidents. This document describes the risk monitoring capabilities of Data Security Audit.
Viewing Risk List
1. Log in to the TencentDB for SQL Server console.
2. Select DSAudit in the left sidebar.
3. On the DSAudit page, click Risk.

4. On the Risk Tag page, you can query data security risks that have triggered risk policies, including Risky Name/Type, Threat Level, Instance ID/Name, Database Account, Detection Time, and Processing Status.
Risk Details
On the Risk Tag page, locate the target risk and click Risk Name to view its details.
Risk Handling
Marking as Ignored
Mark the status of risk items with excessive operation permissions to eliminate interference in risk statistics.
Note:
If the risk handling status is marked as ignored, the risk will not be included in risk statistics.
1. On the Risk Tag page, you can handle target risks individually or in batches.
To handle a single risk: select the risk named Excessive Operation Permission Scope, and click Mark as Ignored in the Operation column.
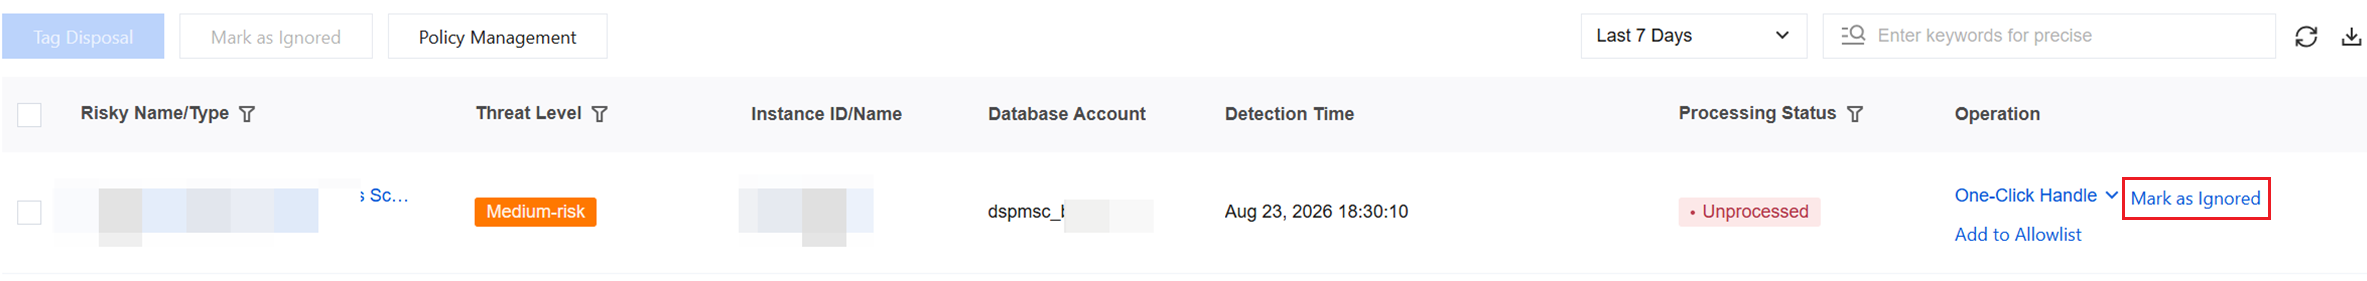
To handle risks in batches: select multiple risks named Excessive Operation Permission Scope, and click Mark as Ignored.
2. In the pop-up window, click OK to mark the risk as ignored.
Adding Allowlists
Note:
After the risk allowlist policy rule takes effect, the behavior will no longer trigger risks.
1. On the Risk Tag page, select the risk named Excessive Operation Permission Scope, and click Add to Allowlist in the Operation column.
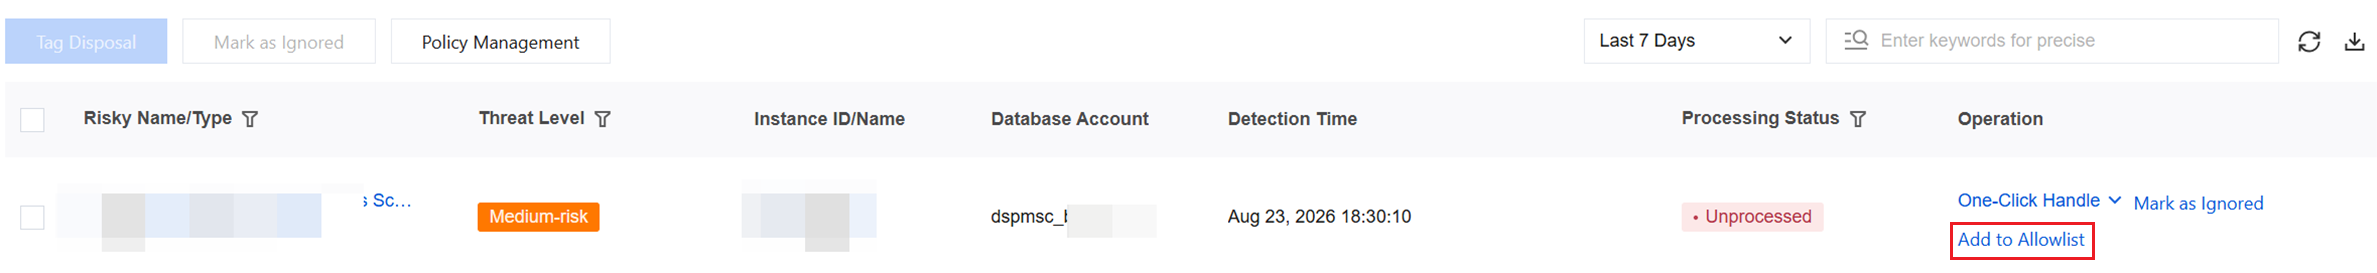
2. In the pop-up window, review the allowlist policy content. After confirming that it is correct, click OK to add the policy information triggered by the risk to the allowlist.
Marking as Resolved
Note:
After the risk handling status is marked as processed, the risk will not be included in risk statistics.
Update the status of risks for which emergency response has been completed to close the handling loop.
1. On the Risk Tag page, select one or more target risks and click Tag Disposal.
2. In the pop-up window, review the risk information. After confirming that it is correct, click OK to mark the risk as handled.
One-Click Handling
For different risk items, you can use One-Click Handle to handle risks.
On the Risk Tag page, select the target risk and click One-Click Handle in the operation column. You can then handle the risk using the preset handling actions.
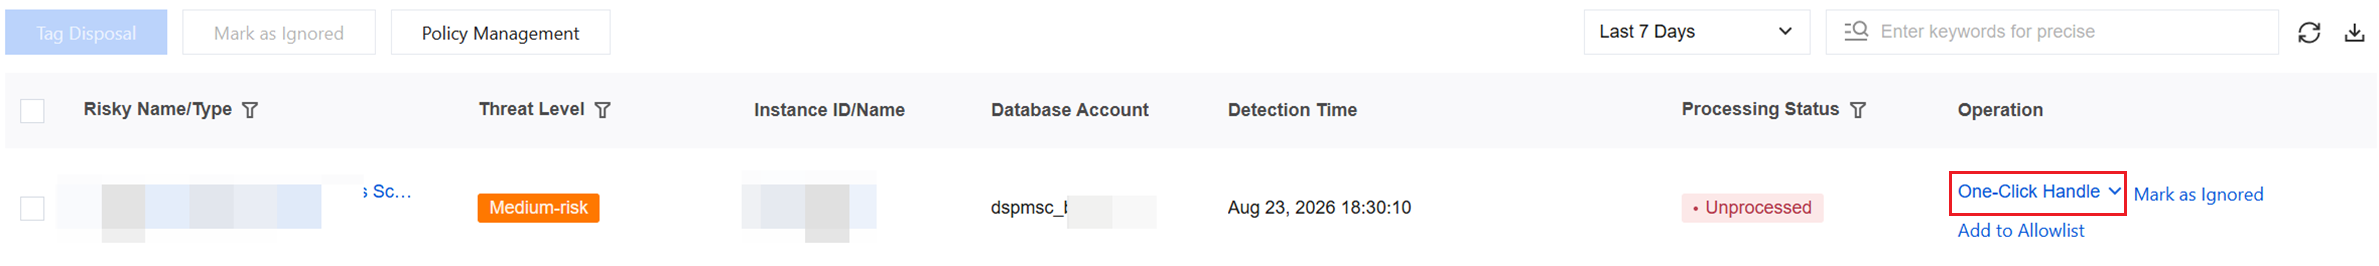
Risk Policy Configuration
1. Log in to the TencentDB for SQL Server console.
2. Select DSAudit in the left sidebar.
3. On the DSAudit page, click Risk.
4. On the Risk Tag page, click Policy Management.
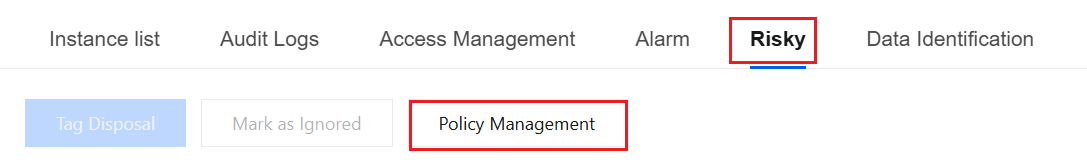
5. All built-in preset risk policies are displayed in the pop-up sidebar. You can enable/disable risk policies, adjust their threat levels, and modify their content on this page.
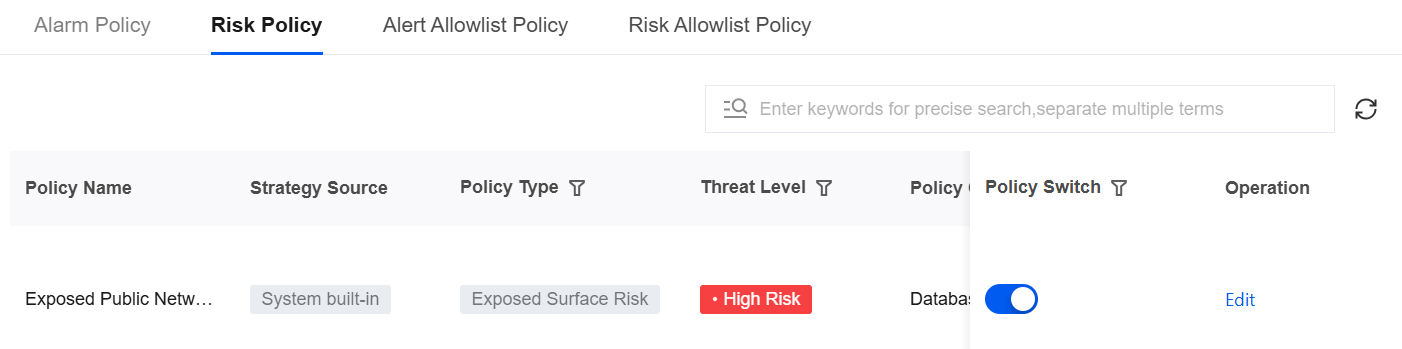
Enabling or Disabling Risk Policies
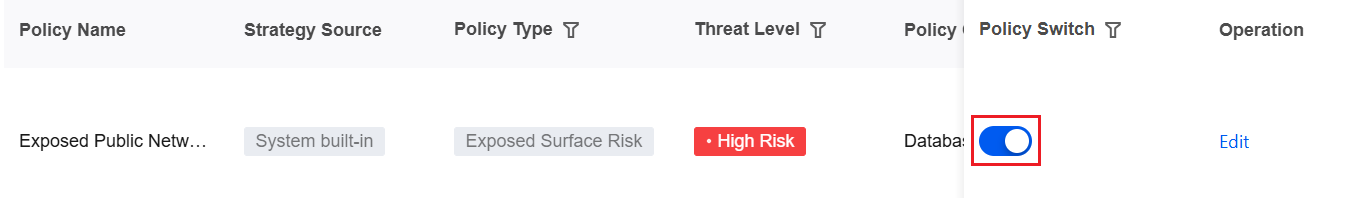
On the Risk Policy Tag page, find the target risk policy and click the switch in the Policy Switch column to enable or disable the risk policy.
Editing Risk Policies
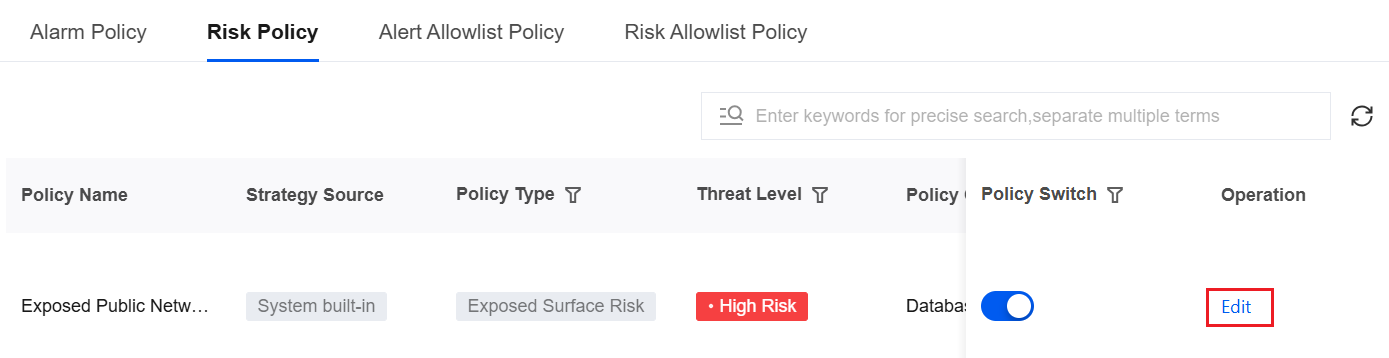
1. On the Risk Policy Tag page, find the target risk policy and click Edit in the Operation column.
2. In the pop-up window, you can modify Threat Level and Policy Content (non-service accounts).
Bantuan dan Dukungan
Apakah halaman ini membantu?
Anda juga dapat Menghubungi Penjualan atau Mengirimkan Tiket untuk meminta bantuan.
masukan