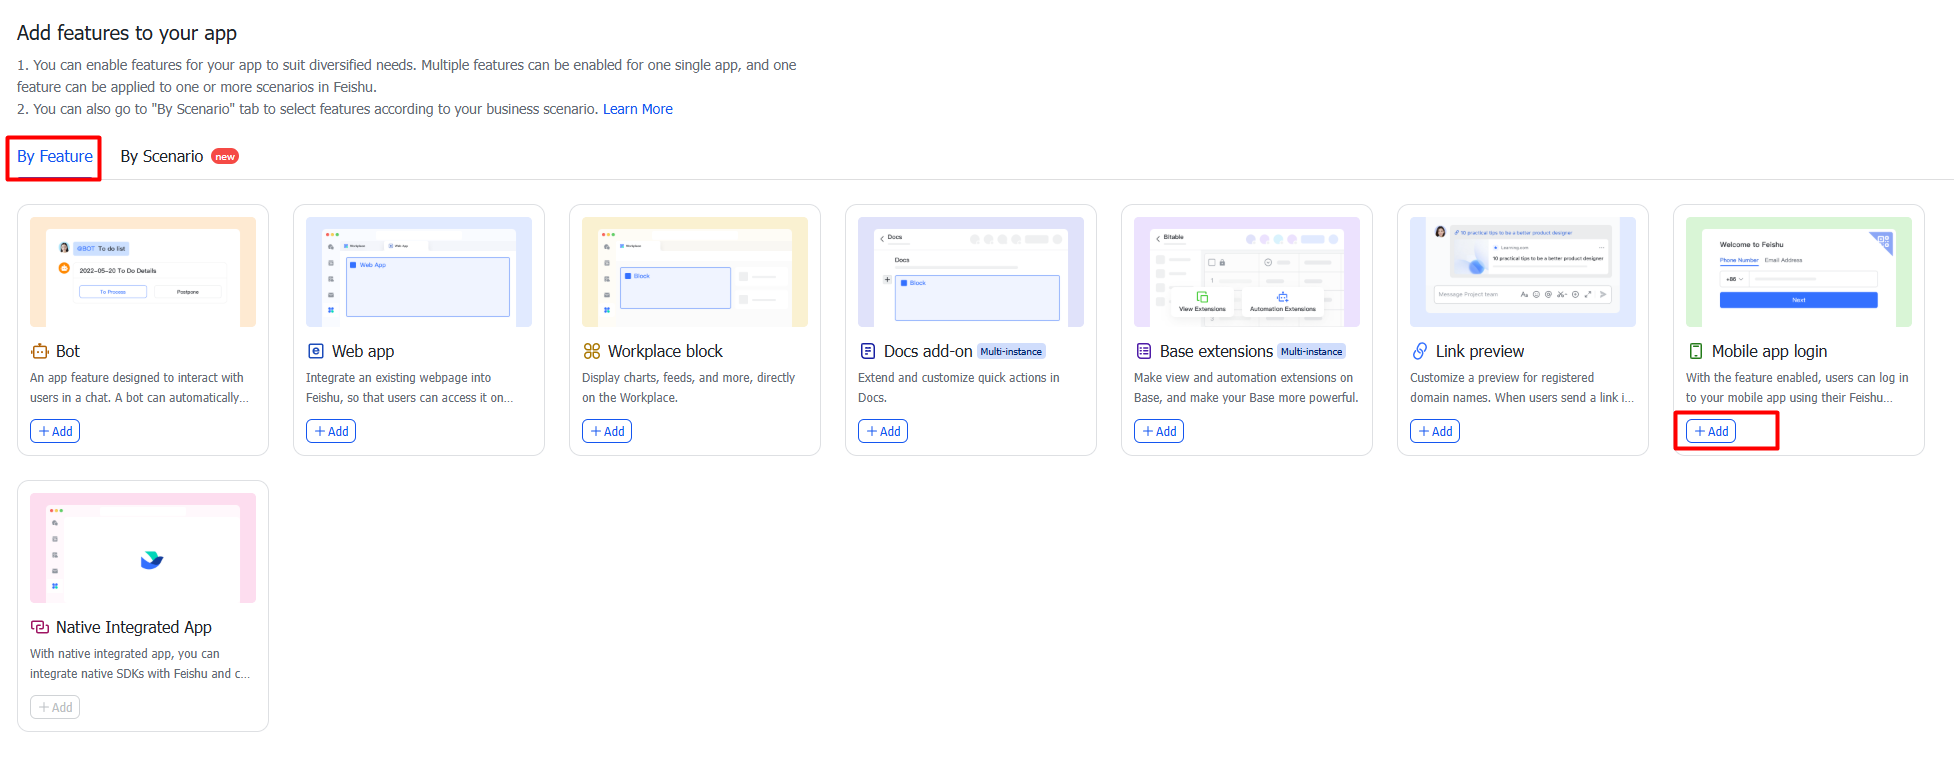
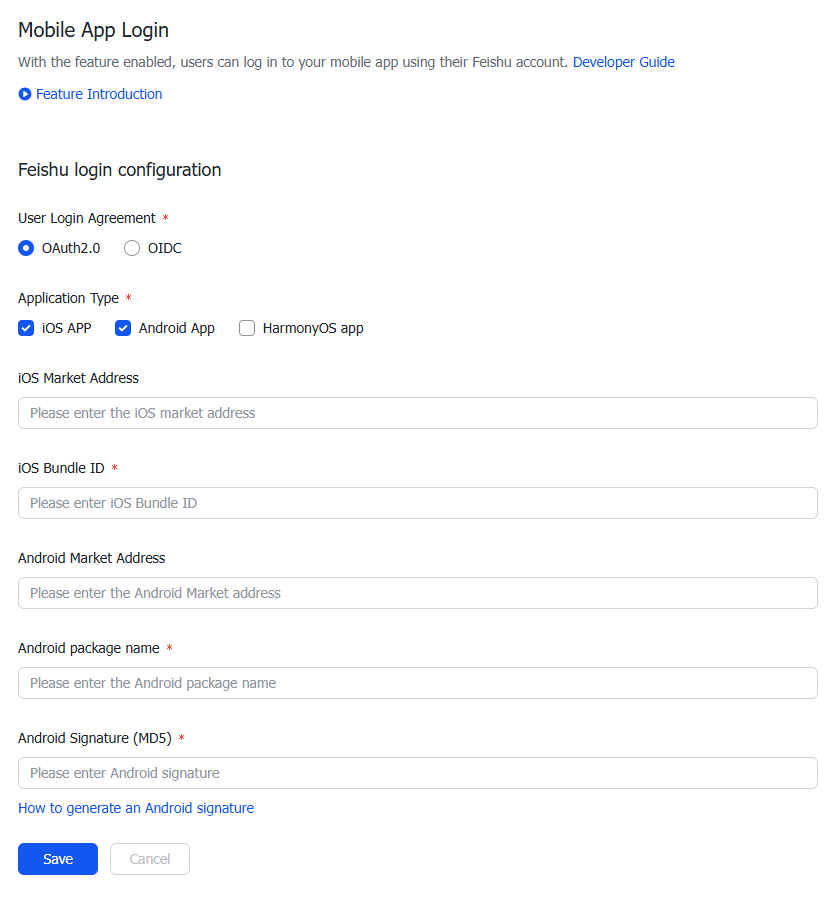
To use Feishu authentication on iOS, contact the iOA projecttechnical supportteam. We need to configure the login parameters in the backend and can provide an iOS login Demo.
For iOA SaaS Feishu integration, it is recommended to use Option 1: Feishu Authentication.
Type
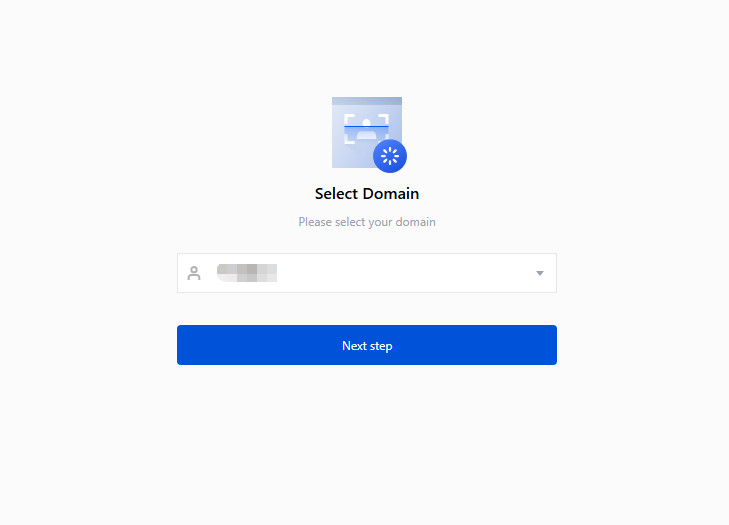
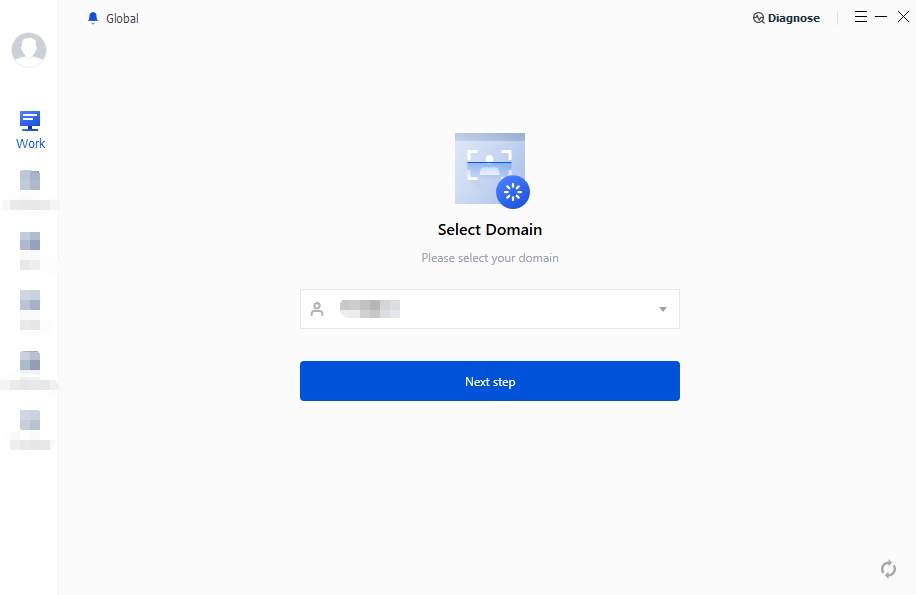
Select Organization Domain
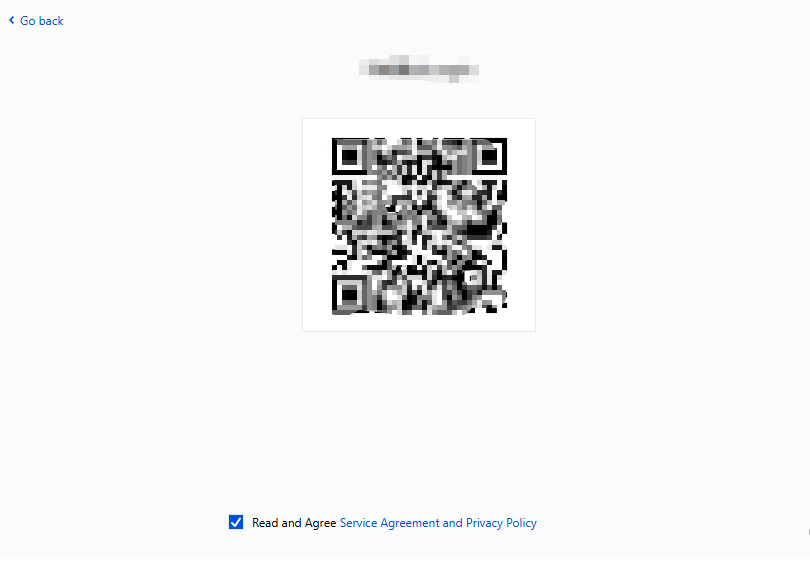
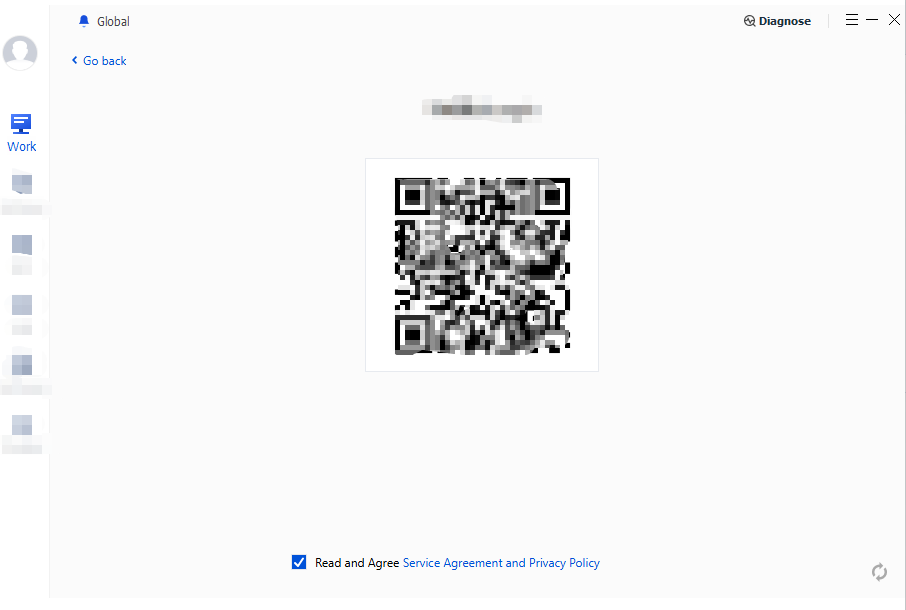
Login Effect
Browser
Client
2. Feishu Authentication Preparation
2.1 Configuring Feishu Information
1. If you are a first-time user and have not created a self-built enterprise application:
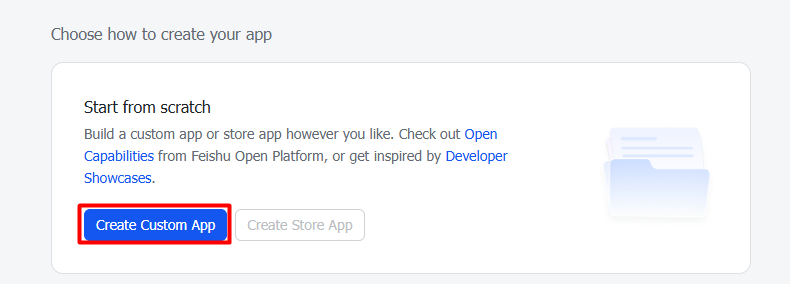
1.1 If you have not created a self-built enterprise application, create one by logging in to the Feishu Open Platform, selecting Self-built Enterprise Application, and clicking Create Custom App.
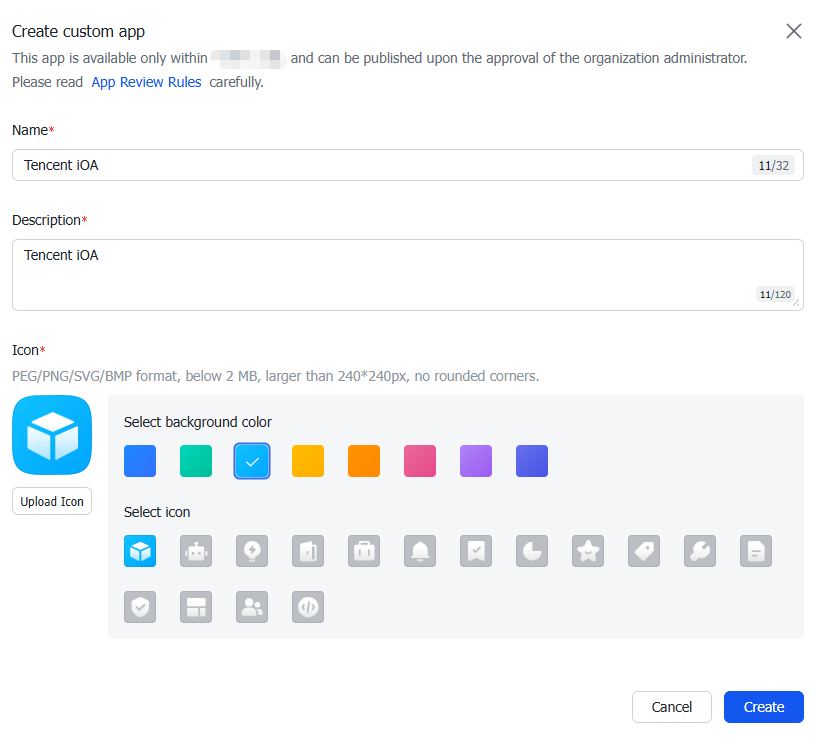
1.2 In the Create Self-built Enterprise Application window, configure the relevant parameters and click Create to complete the creation.
2. If you have not activated a Feishu developer account:
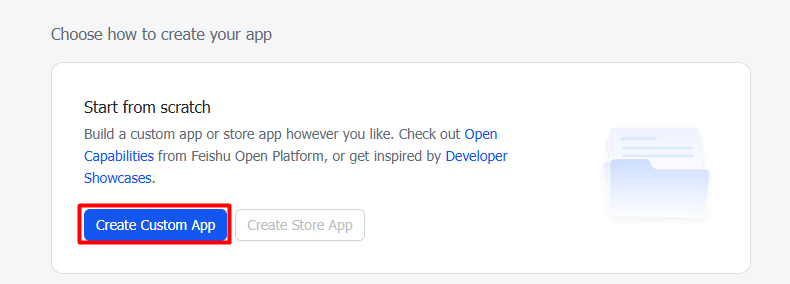
2.2 In the Developer Console, select Self-built Enterprise Application and click Create Custom App.
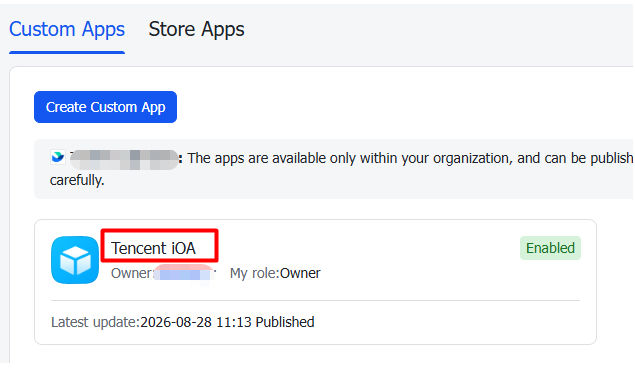
2.3 Application name example: Tencent iOA; Application description: xxxx (any description).Credentials & Basic Info
2.2 Obtaining App ID and App Secret
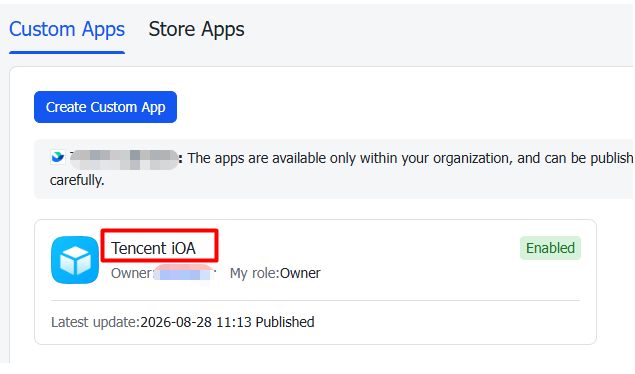
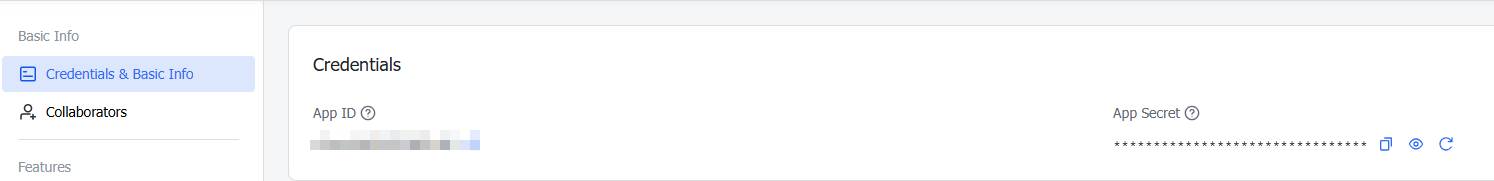
1. On the Enterprise Self-built Application page, click the self-built application you just created to go to the application details page.
2. On the Credentials & Basic Info page, select Credentials to get the App ID and App Secret. Note that the App ID and App Secret from Feishu correspond to the App ID and App Secret on the iOA console, respectively.
2.3 Configuring the Redirect URL
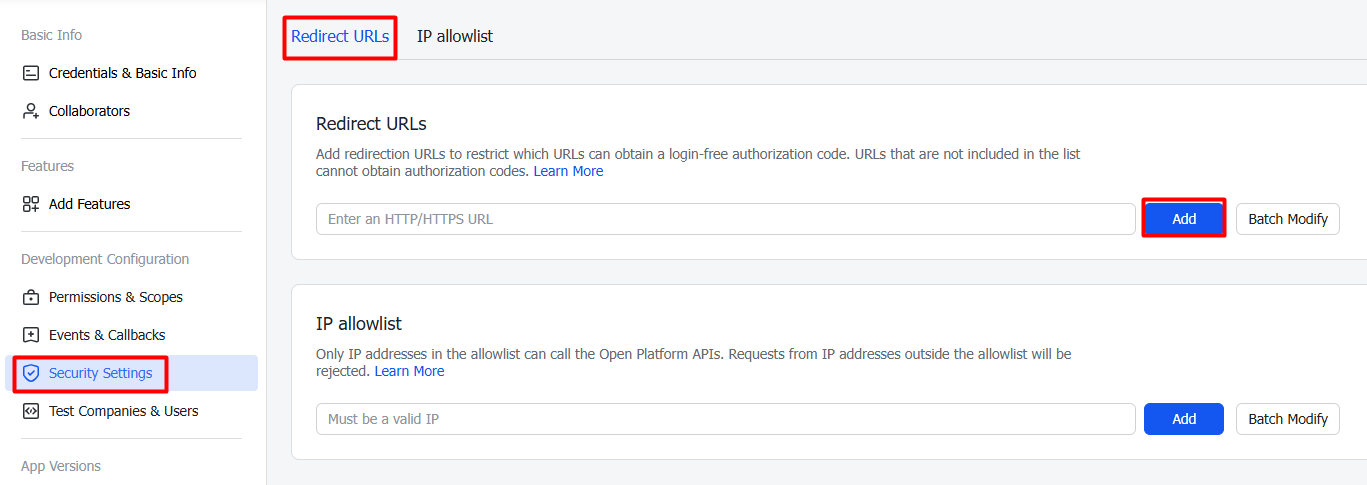
1. On the Credentials and Basic Information page, click Security Settings.
2. On the Redirect URL page, enter the following iOA gateway callback domain and click Add to add it to the redirect URL list.
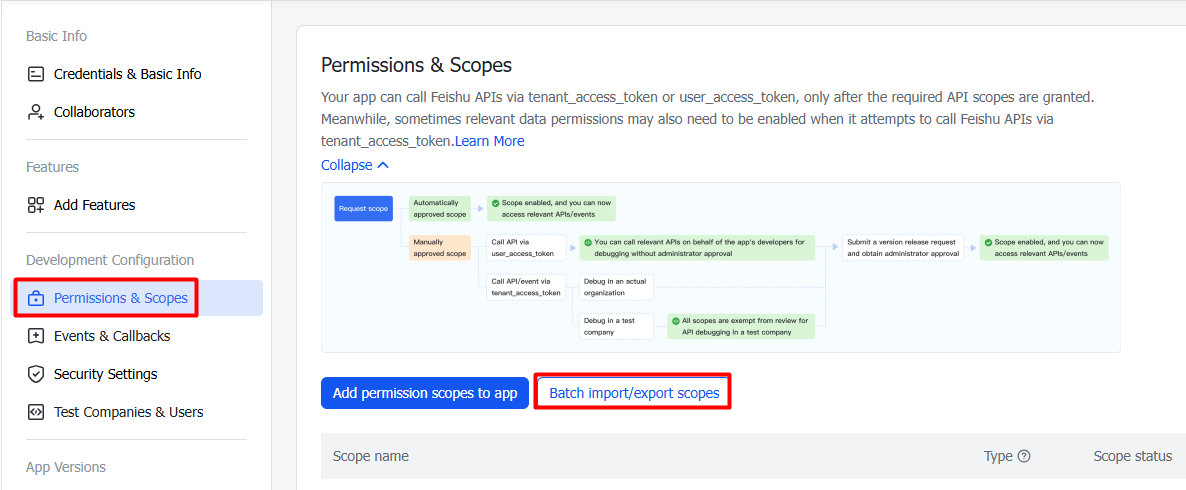
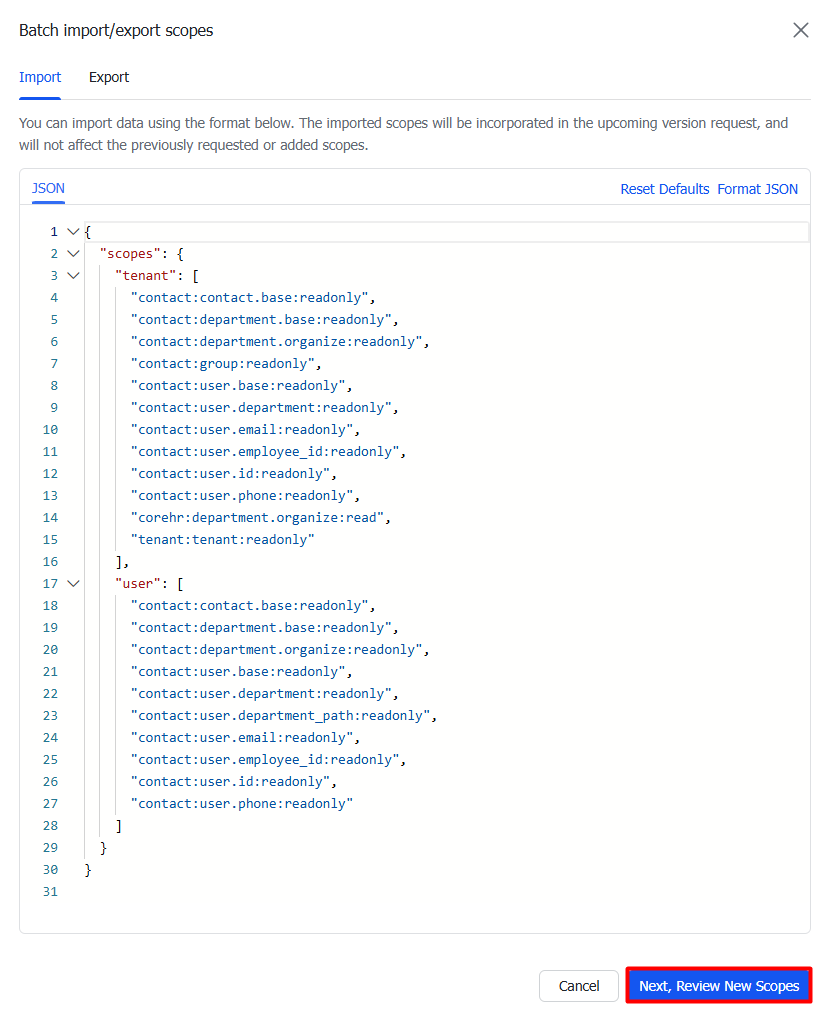
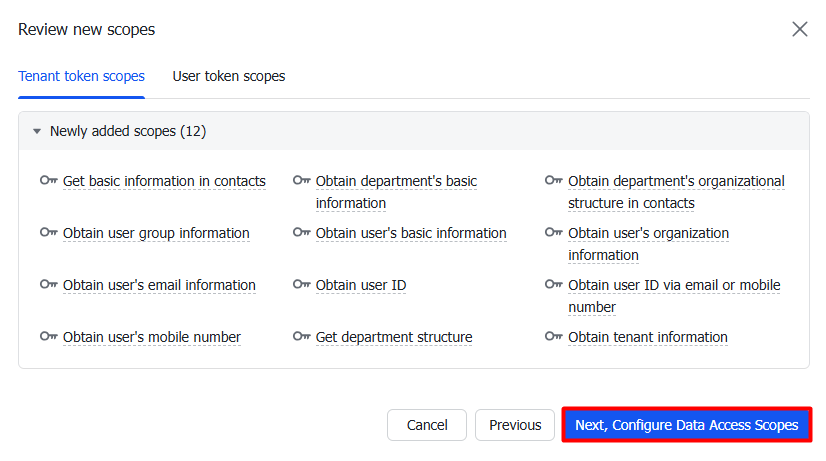
2. In the batch import/export permissions dialog, enter the following JSON and click Next, Review New Scopes.
{
"scopes":{
"tenant":[
"contact:contact.base:readonly",
"contact:department.base:readonly",
"contact:department.organize:readonly",
"contact:group:readonly",
"contact:user.base:readonly",
"contact:user.department:readonly",
"contact:user.email:readonly",
"contact:user.employee_id:readonly",
"contact:user.id:readonly",
"contact:user.phone:readonly",
"corehr:department.organize:read",
"tenant:tenant:readonly"
],
"user":[
"contact:contact.base:readonly",
"contact:department.base:readonly",
"contact:department.organize:readonly",
"contact:user.base:readonly",
"contact:user.department:readonly",
"contact:user.department_path:readonly",
"contact:user.email:readonly",
"contact:user.employee_id:readonly",
"contact:user.id:readonly",
"contact:user.phone:readonly"
]
}
}
3. In the Confirm Import Permissions dialog, click Next, Configure Data Access Scopes.
2.4.2 Manually Granting Permissions
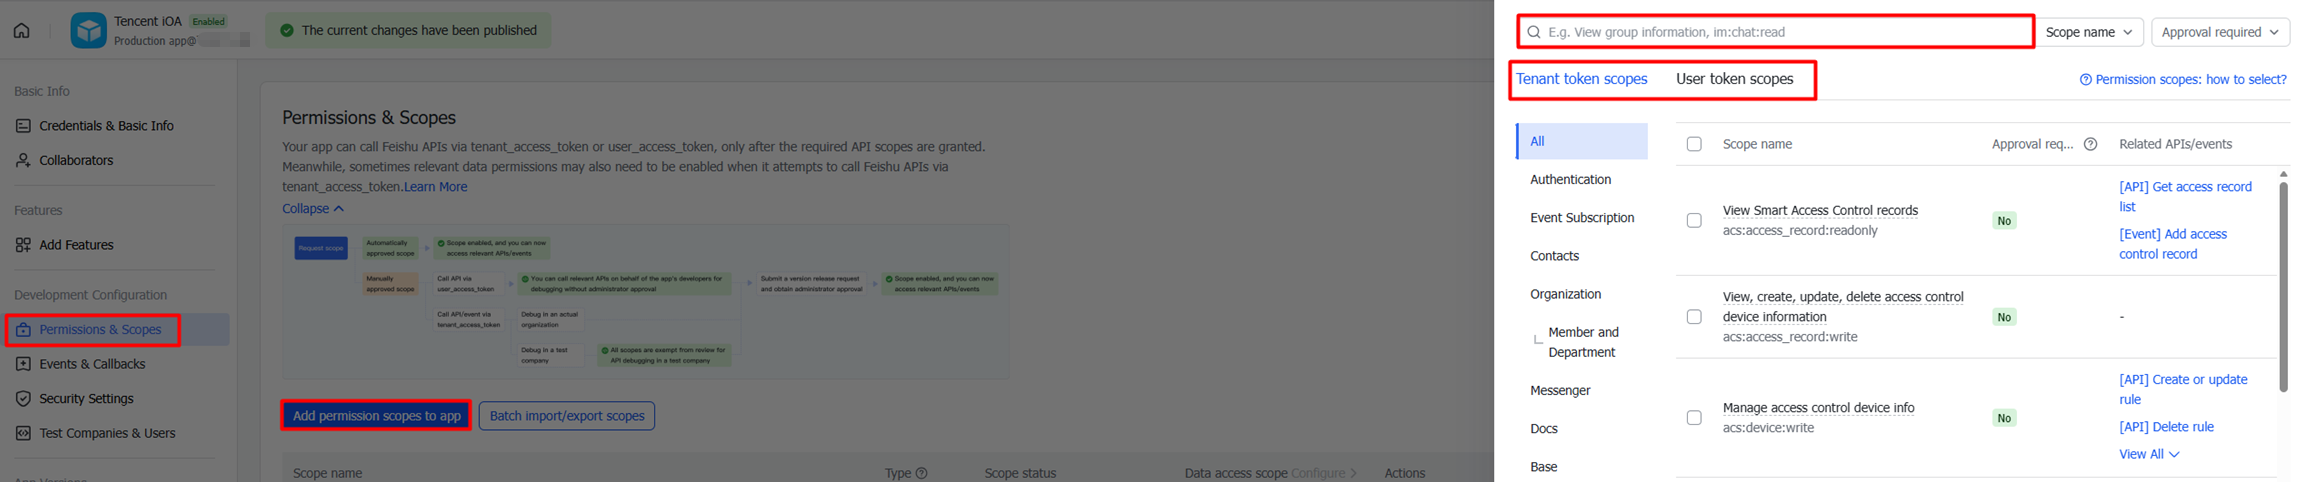
1. On the Permission Management page, click Add permission scopes to app Permissions & Scopes and select the permissions required by the application. It is recommended to use the English version for queries first.
Attention:
All of the following permissions must be activated. If they are not all activated, configuration-related error messages may occur.
In Permissions & Scopes > Add permission scopes to app, if the queried permissions include both application identity permissions and user identity permissions, both must be selected.
Example: Query contact:user.base:readonly. If contact:user.base:readonly exists in both application identity permissions and user identity permissions after the query, permissions must be activated for both.
Permission Name
Permission Name in Chinese
contact:user.department_path:readonly
Obtain the department path of a member.
contact:user.base:readonly
Obtain basic user information.
contact:contact.base:readonly
Obtain basic contact information.
contact:department.organize:readonly
Obtain contact department organizational structure information.
contact:department.base:readonly
Obtain basic department information.
corehr:department.organize:read
Obtain department organizational structure information.
contact:group:readonly
Obtain user group information.
contact:user.department:readonly
Obtain user organizational structure information.
contact:user.email:readonly
Obtain user email information.
contact:user.employee_id:readonly
Obtain user ID.
contact:user.id:readonly
Obtain user ID by mobile number or email.
contact:user.phone:readonly
Obtain user mobile number.
tenant:tenant:readonly
Obtain enterprise information.
2. After selecting the target permission, click Confirm Permission Activation in the Operation column to select the required permissions for the application.
Note:
After configuring permissions, you must republish the application for the changes to take effect.
2.5 Publishing an Application
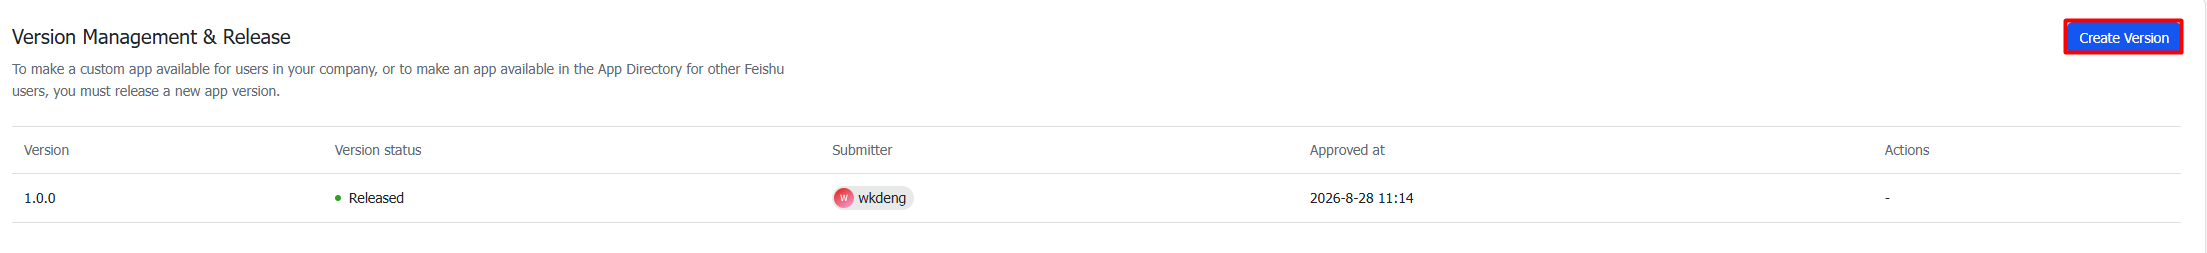
1. On the Permission Management page, click Version Management and Release.
2. On the Version Management and Release page, click Create Version in the upper-right corner.
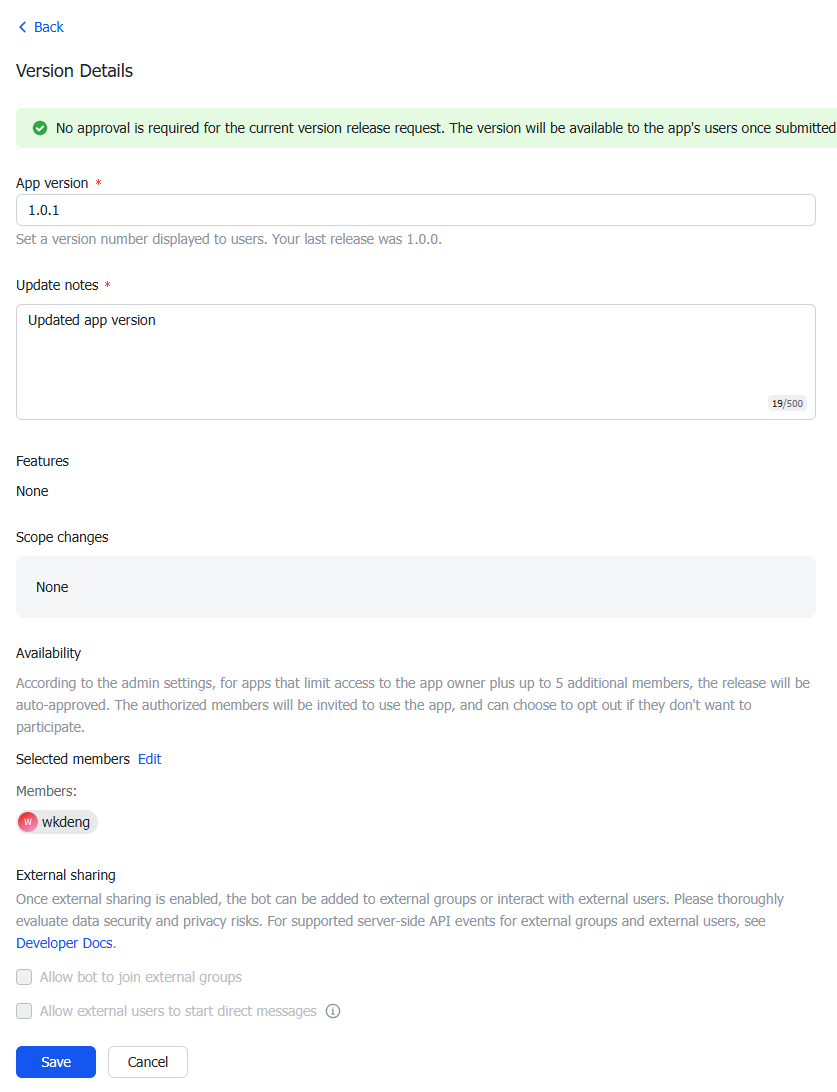
3. On the version details page, enter the application version number (for example, 1.0.0) and update description, set the availability status, and click Save.
Attention:
Availability scope: select all employees.
4. After saving, click Publish.
Note:
After the application is submitted, the enterprise administrator will review it.
The review result will be sent to you through Feishu and the developer console.
2.8 Enabling Email/Phone Number Account Identity Association (Optional)
Note:
If you need to enable SMS verification codes or email verification codes as an instance of two-factor authentication/challenge authentication, we recommend that you grant the synchronization permission for phone numbers or email addresses when syncing fields from Feishu. When adding SMS verification codes or email verification codes in the iOA console, use the phone numbers/email addresses synced from Feishu as the basis for field mapping and identity authentication.
1. Log in to the Feishu Open Platform, select Custom Apps, and click the target self-built application.
2. On the application details page, click Permission Management and scroll down to Permission Configuration.
3. In the Permission Configuration module, enable the following two features separately:
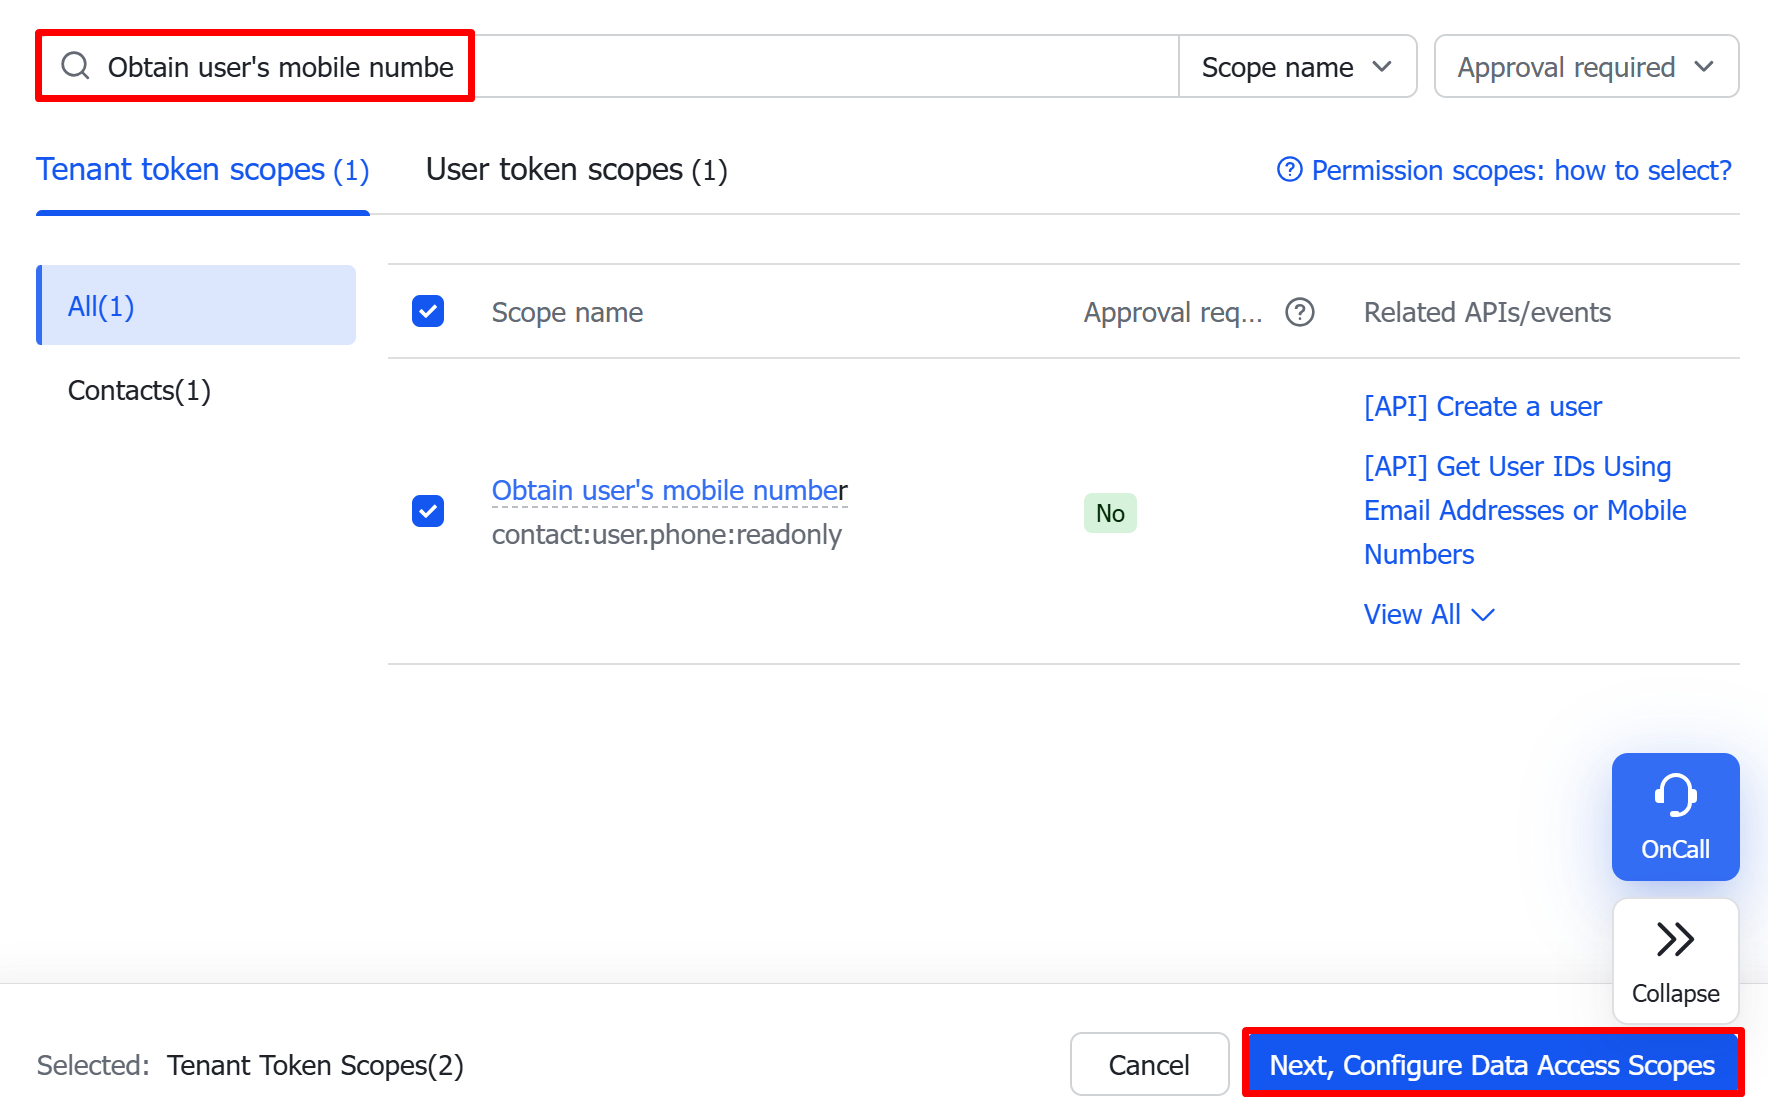
To enable the phone number account identity association feature, search for Obtain user's mobile number and click Activate Permission.
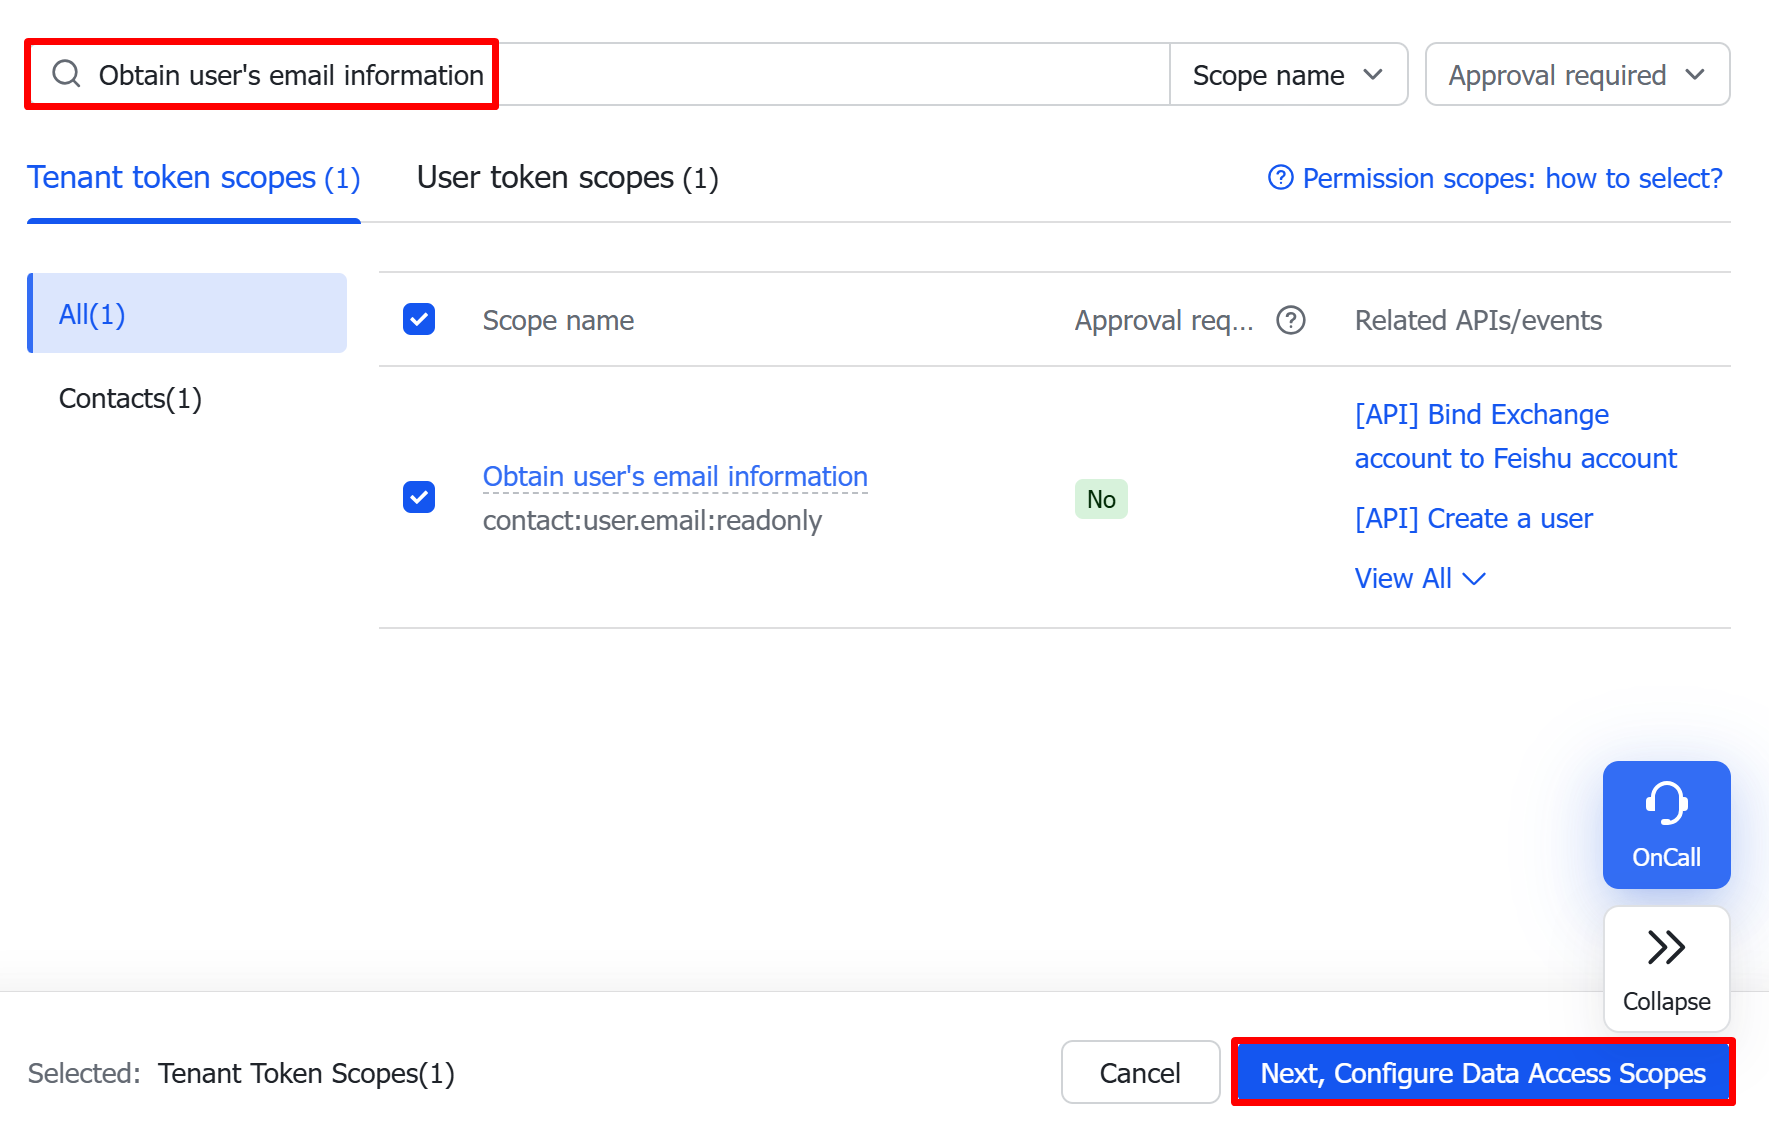
To enable the email account identity association feature, search for Obtain user's email information and click Activate Permission.
4. After configuring the above permissions, you need to republish the application version for the changes to take effect.
Customize the interval for pulling the latest organizational structure.
Performing a Connectivity Test
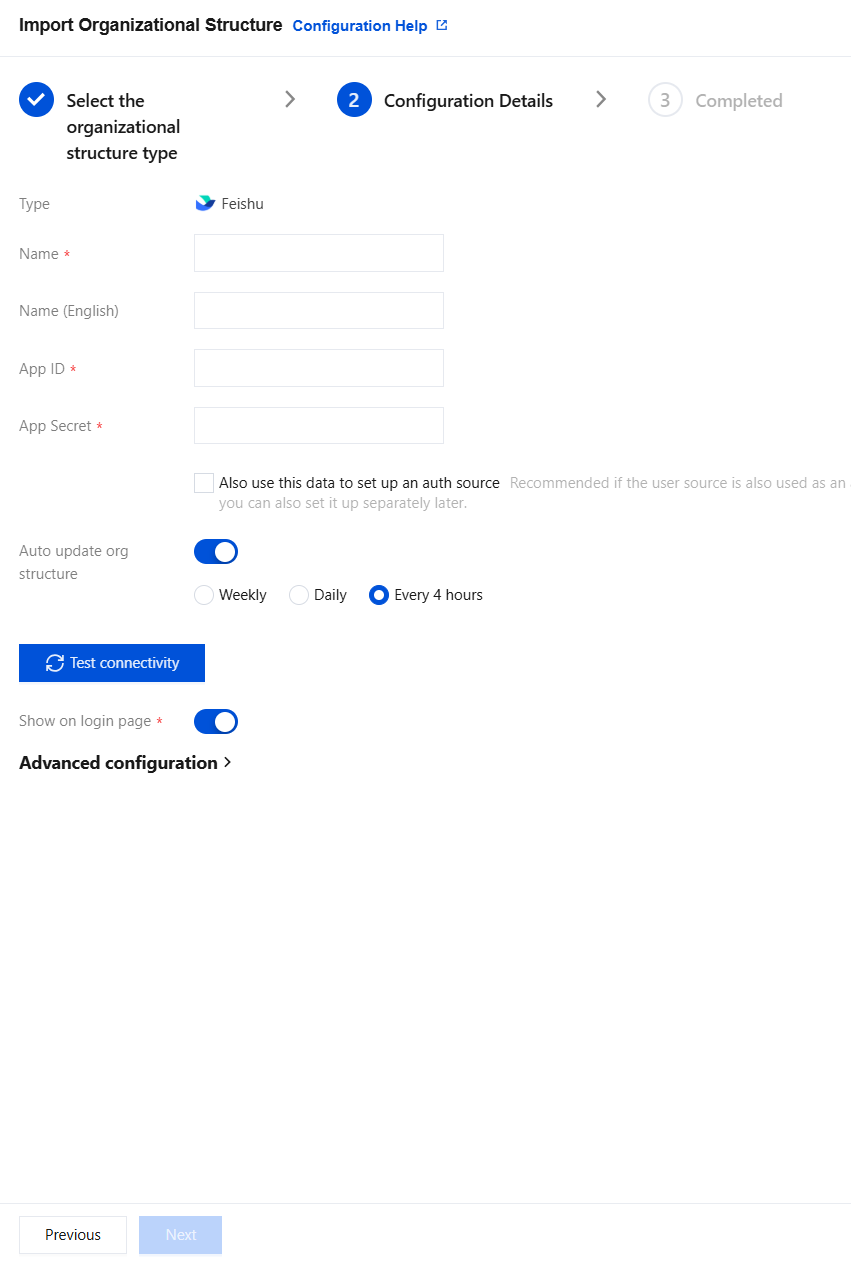
After entering the App ID and App Secret, you can perform a connectivity test, which also checks whether the basic configuration is valid.
Client Login Display
Whether to display the DingTalk organizational structure entry on the iOA client login page.
Enable: The iOA client login page displays the DingTalk login option, allowing users to log in with DingTalk.
Disabled: The iOA client login page does not display the DingTalk login option, and users cannot log in with DingTalk.
Sync Architecture Nodes
Supports on-demand synchronization of the organizational structure based on department IDs. Click Add to select the departments to synchronize, which are queried and expanded level by level in real time without synchronizing the entire organizational structure.
Root department ID: If only a specific department is needed, enter the correct department ID. Do not modify it unless necessary. If data has been synchronized normally, arbitrary changes may lead to data exceptions.
Department hierarchy completion: Click
to enable this feature. When this feature is enabled, the system automatically completes all parent department levels of the selected department. When this feature is disabled, only the synchronized departments are mounted under the root node.
User Attribute Field Mapping
Do not modify unless necessary.
If the fields are not mapped, the system-defined status will be used, where 0 indicates an abnormal user status and 1 indicates a normal user status.
Mapping supports three data types, and you must specify the value for the normal status:
1. For Bool and String types, equal values are associated with state 1, and unequal values are uniformly associated with state 0.
2. For the Int type, equal values are associated with state 1, while other values are retained by default.
In attribute mapping, if a mapping field does not exist or you do not want to synchronize the corresponding field, enter any non-existent attribute name, and the corresponding attribute will be set to empty during synchronization.
5. Click Test Connectivity. After the test passes, click Next and Save.
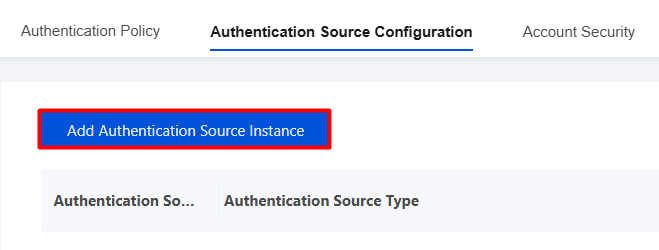
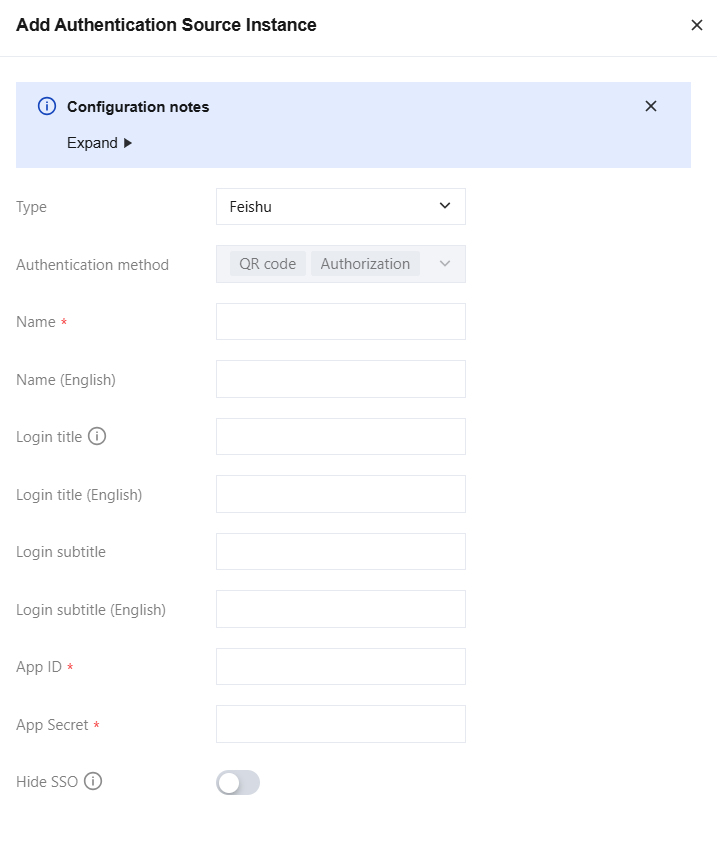
2. On the Authentication Source Configuration page, click Add Authentication Source Instance.
3. On the Add Authentication Source Instance page, select Feishu as the type, configure other parameters, and click Save.
Note:
App ID: The Feishu App ID.
App Secret: The Feishu App Secret.
3.3 Setting Authentication Policies
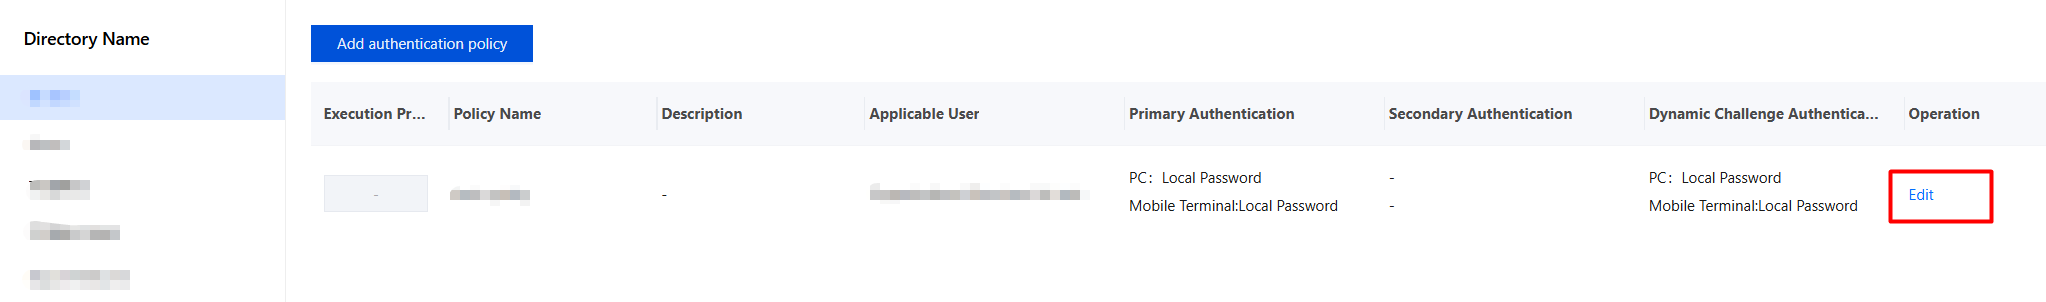
1. On the Identity Security Management > Authentication Policy page, select the target directory and click Edit.
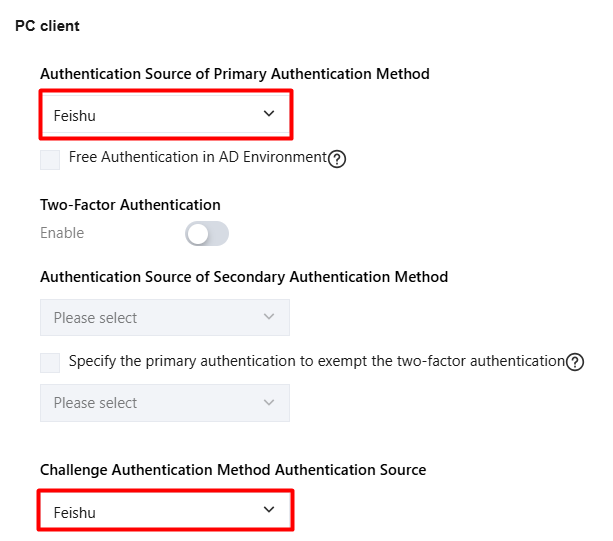
2. On the Edit Authentication Policy page, set the primary authentication source and the challenge authentication source for the PC client.
Note:
If you want to use password-free login for apps within Feishu, you also need to configure the primary and challenge authentication sources for the mobile client. The configuration method is the same as that for the PC client.